EMBEDDED ZERO TRUST ARCHITECTURE FOR PHYSICAL SECURITY

Zero Trust.
From Source to Decision.

PSG's unified Zero Trust platform spans access control, intrusion detection, and video surveillance - from command-and-control software to far-edge hardware, delivering verified data for AI and automation.

PRODUCTS
Unified Security Platforms

Unified Security Platforms

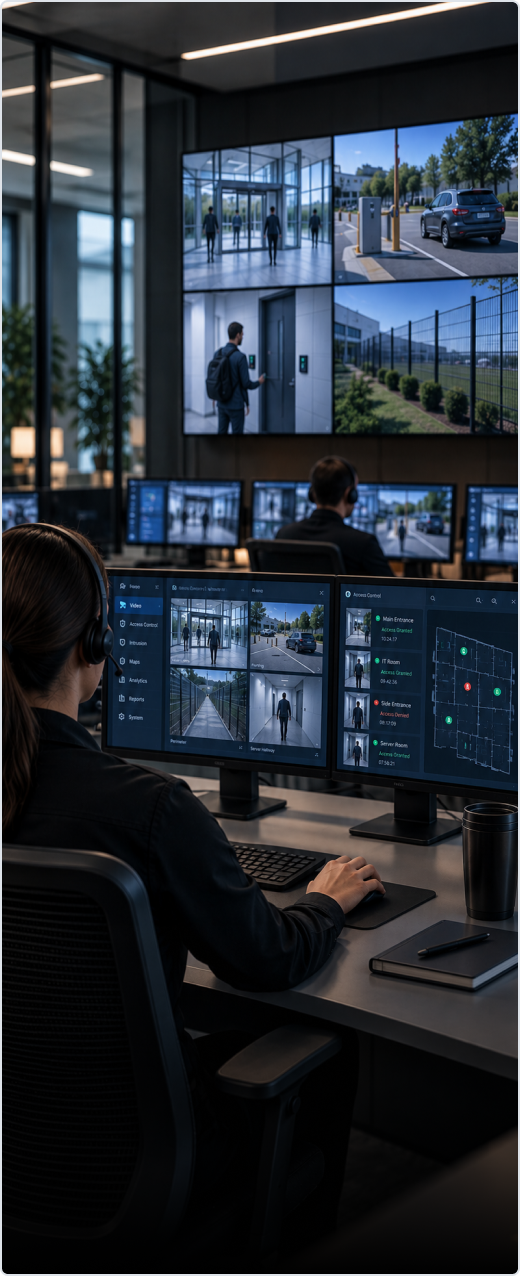
Command and control for intrusion, access, and video in one operator view.
View category
Self-Contained Systems

Self-Contained Systems

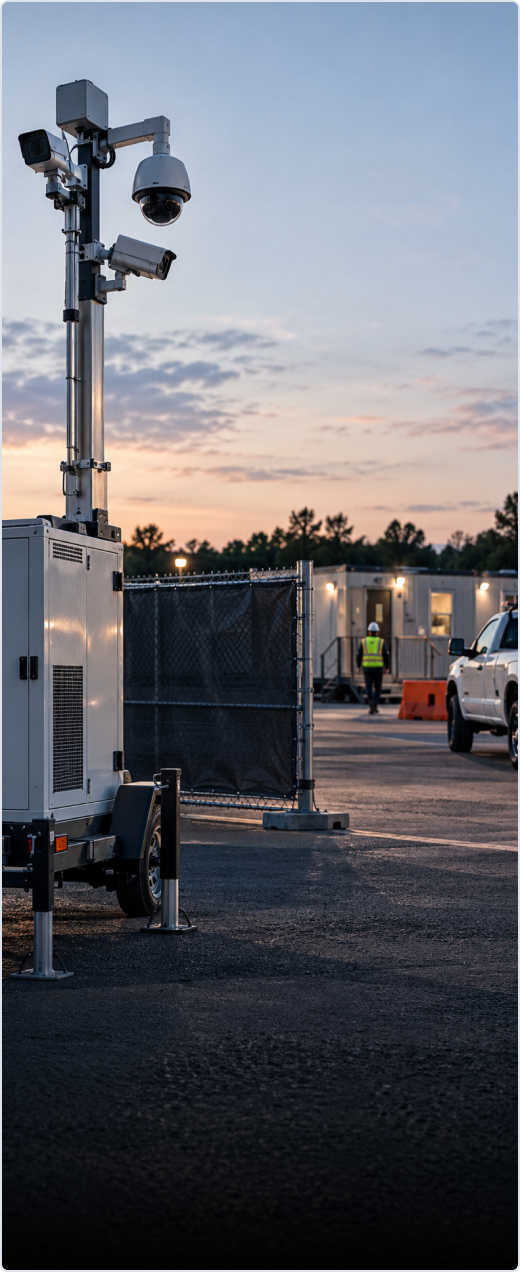
Complete systems for a defined deployment, from a SCIF to a portable perimeter.
View category
Video Management

Video Management

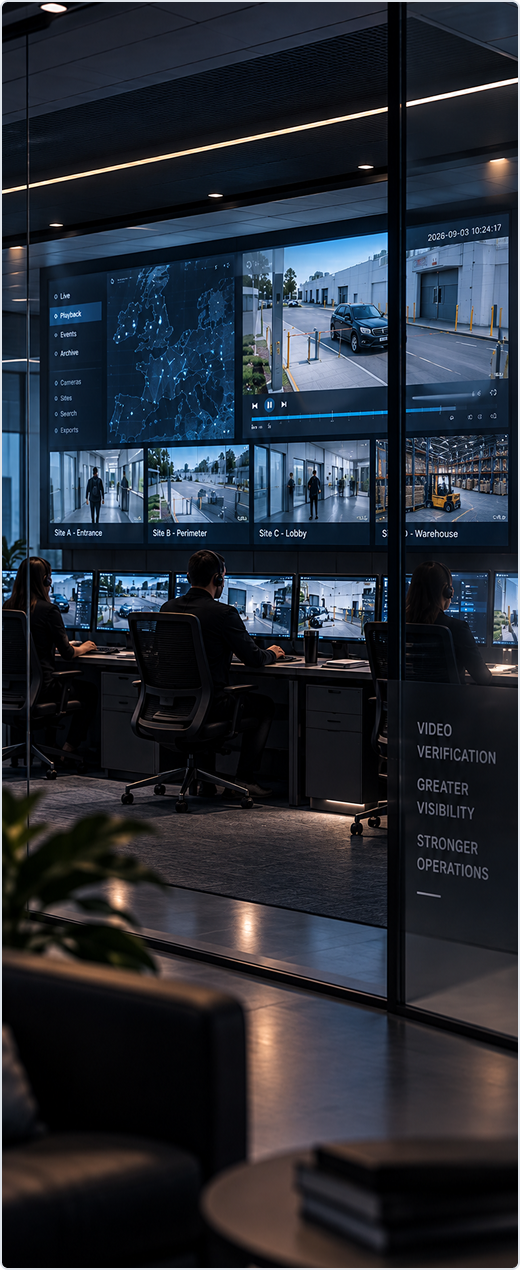
Video verified live at the scene, from the camera to the operator and the archive.
View category
Intelligent Controllers

Intelligent Controllers

Zero Trust at the door and the fence line, on the wiring already installed.
View category
Cybersecurity

Cybersecurity

Compliance enforcement and a verified data lake that keep every layer verified.
View category
WHERE PSG FITS

The trust layer everything else builds on.

IT protects information. OT protects operations. Physical Security protects people. As they converge, every sensor, reader, camera, and controller has joined the cyber attack surface, most on signaling designed before that was true.

Network and OT monitoring tools observe activity above the device layer. PSG establishes cryptographic trust beneath it, in the device itself at Purdue Levels 0 and 1. The physical security, industrial control, and building automation platforms you run receive authenticated, verified data from the source. PSG strengthens the ecosystem. It does not replace it.

  • Enterprise Consumers

    SOC, SIEM, cloud, AI and modeling. Consumes verified data.

    Purdue 4 to 5

    Third party

  • IT and OT Operations

    Command and control, video management, compliance, data lake.

    Purdue 2 to 3

    PSG

  • Acquisition and Control

    Panels, controllers and scene authentication at the edge.

    Purdue 1

    PSG

  • OT Edge

    Cameras, sensors, readers and door hardware, new or already installed

    Purdue 0

    PSG embedded

THE FOUR PILLARS OF VERIFIED SECURITY
Crytographically Identified Devices

Crytographically Identified Devices

Every sensor, reader, controller, camera and field device carries a cryptographic identity and is verified before it joins the system.
Authenticated Data

Authenticated Data

Every security event is authenticated and verified before operators, enterprise systems, automation or AI act on it.
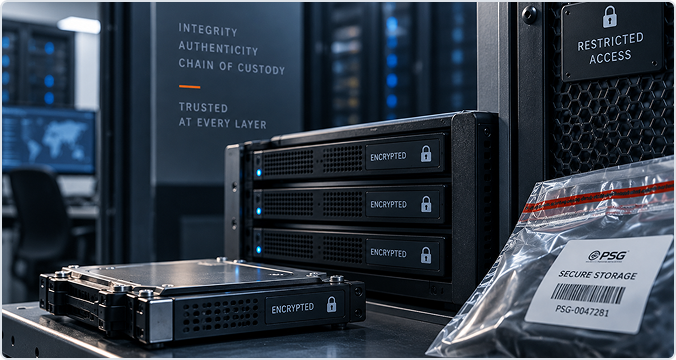
Protected Storage

Protected Storage

Physical security data stays protected from alteration, with authenticity and chain of custody preserved across its lifecycle.
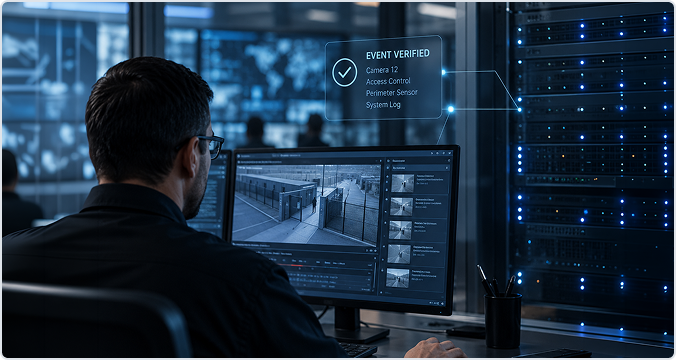
Confident Decisions

Confident Decisions

Operators, automation platforms and AI decide on verified information rather than assumptions. Better data leads to better decisions.
PARTNERS
Partners · OEM and integrator ecosystem

Closing CTA · protected facility-1