

Unified Security Platforms
Command and control for intrusion, access, and video in one operator view.
Zero Trust Architecture
Zero Trust is proven on the network. PSG embeds it in the devices below the network, where readers, sensors and cameras have always been trusted by default.
Authenticated and verified (A-V), edge to enterprise.
Decisions made on data verified at every layer below.
Purdue 4 to 5 · Third party
Deploy, response force
Command and control, video and compliance, working from authenticated data.
Purdue 2 to 3 · PSG
Security operations center (SOC)
ZTA Data Lake
ZTA unified PSE solution: C2, access, intrusion, video, cyber.
C2 GUIs
HPC cluster
Panels, controllers and scene authentication give every signal an identity.
Purdue 1 · PSG
Every pixel verified. Every incident captured.
Extend perimeters for responding teams.
Scene Authentication and DESI embed in any camera, sensor, reader or door hardware.
Purdue 0 · PSG embedded
Premise Control Unit, SCIF Configuration, Portable IDS.
PSG
The trust gap
Zero Trust is a solved problem on the network. Identity, segmentation and monitoring authenticate every user and every request at the enterprise and operations layers. Below the switch, at the levels the Purdue Model calls 0 and 1, the picture is different. The devices that detect an intrusion or open a door still report over supervised loops designed decades ago.
A supervised loop can tell a panel that a wire is intact or that a circuit changed state. It cannot prove the signal came from the intended sensor. A door contact is a closed circuit. A motion sensor is a resistance value. Anyone who reaches the cable can imitate either.
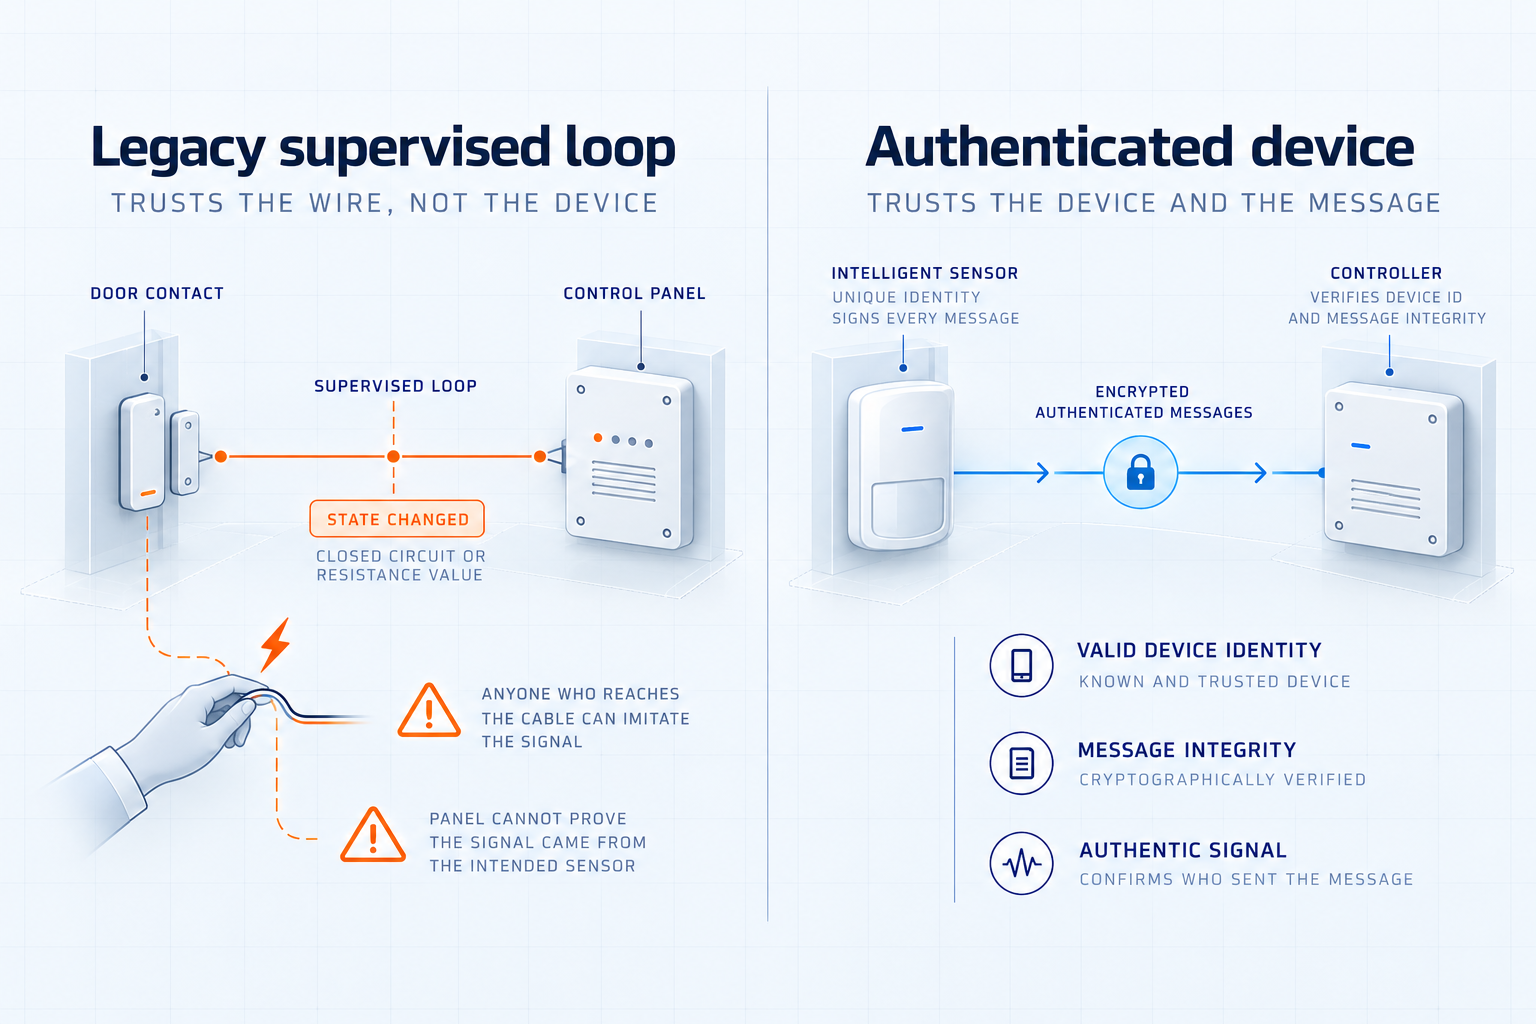
Embedded, not overlay
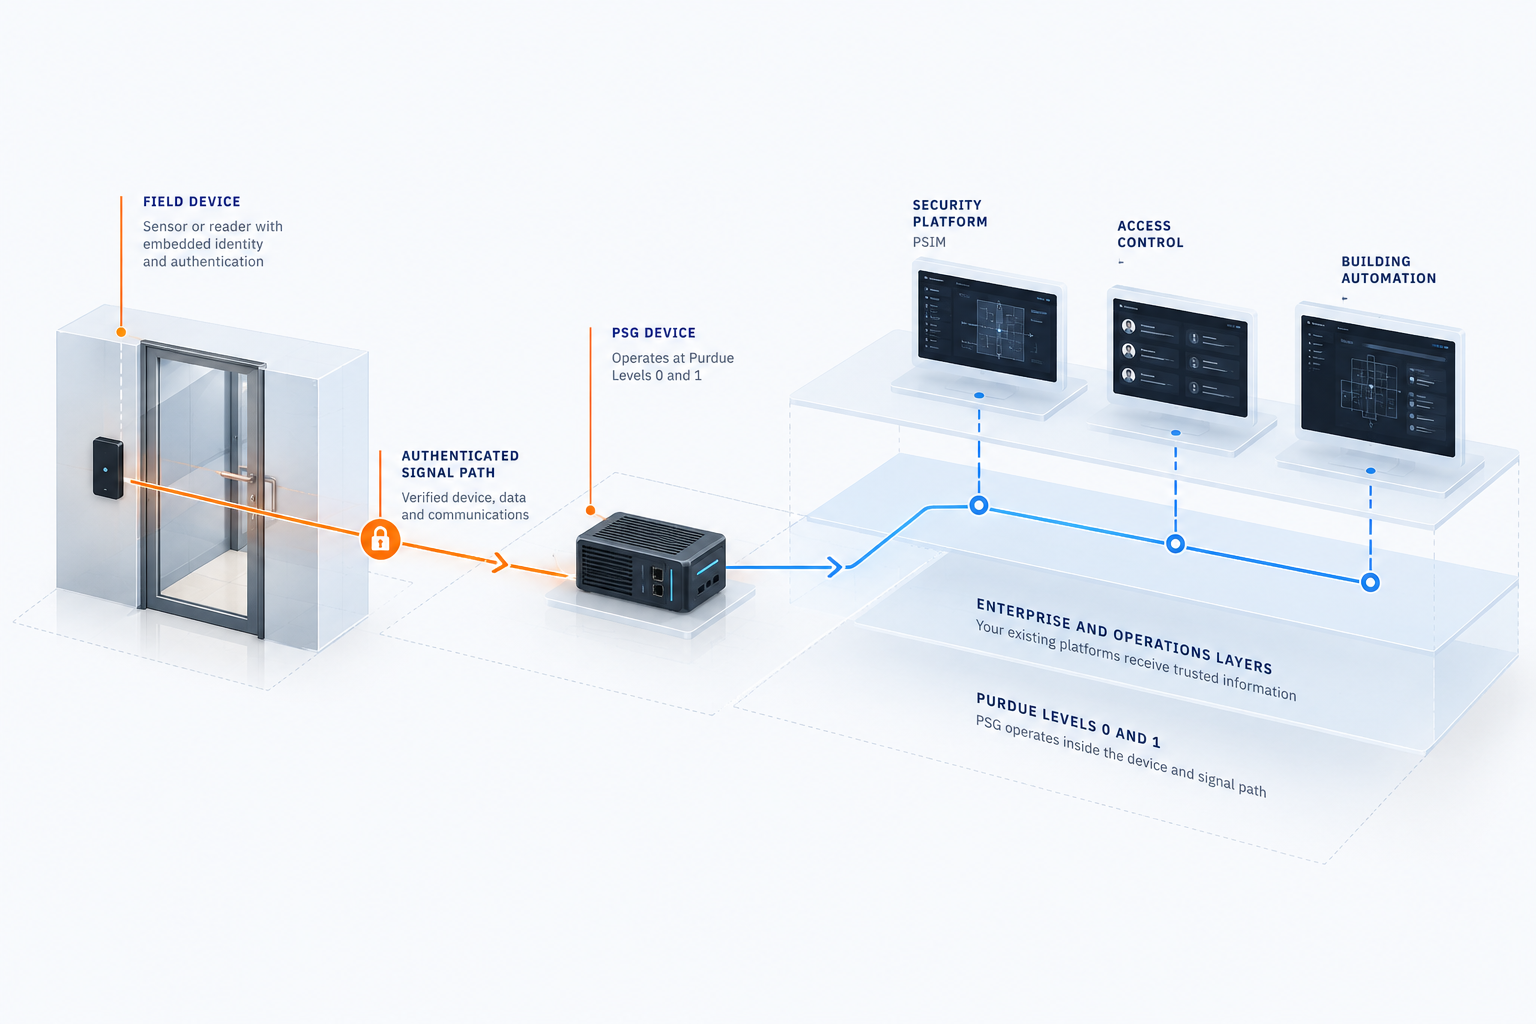
PSG does not compete with network security, PSIM, access control or building automation platforms. Those systems collect, manage and act on information from field devices; they are overlay technologies. PSG operates one layer below, inside the device and the signal path at Purdue Levels 0 and 1.
Every PSG device carries a cryptographic identity, authenticates its communications and verifies its data before anything above it acts. The platforms you already run receive information they can trust instead of information they have to assume. Your existing investment becomes more valuable, not less, and nothing is ripped out to get there.
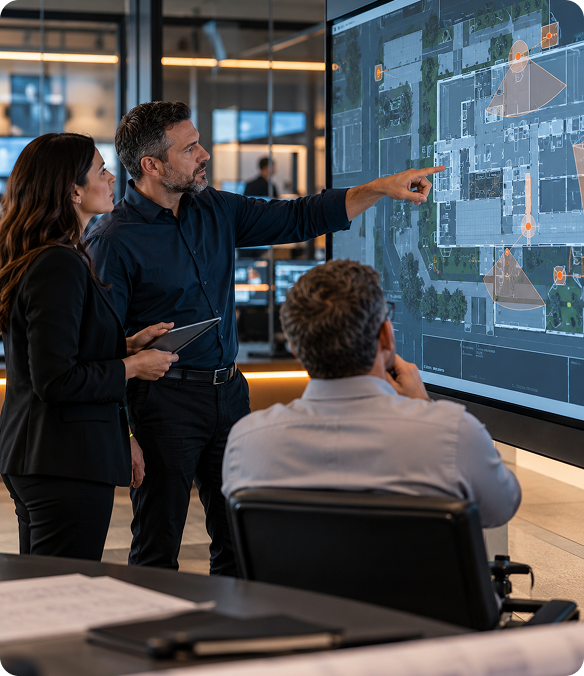
Command and control for intrusion, access, and video in one operator view.
Complete systems for a defined deployment, from a SCIF to a portable perimeter.
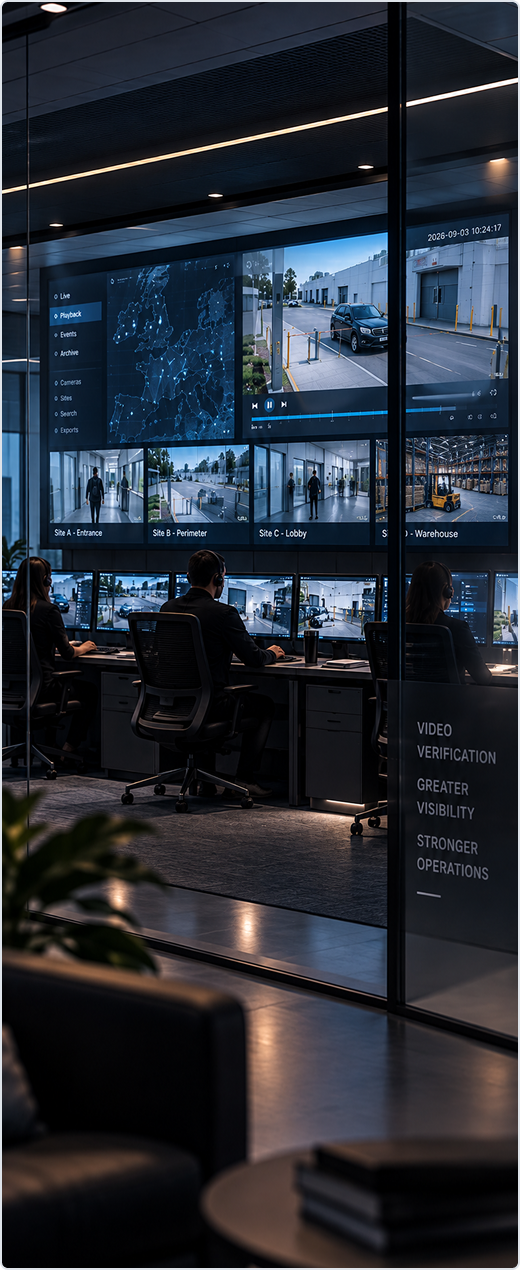
Video verified live at the scene, from the camera to the operator and the archive.
Compliance enforcement and a trusted data lake that keep every layer verified.
Bring us a drawing, or a description of what is installed. Visit with a PSG systems engineer who will map your site to the architecture and show where Zero Trust reaches.