Products

Unified Security Platforms

Command and control for intrusion, access and video in one operator view.

In this category

Side by side

How the three work together

The platform, the operator interface inside it, and the certified command and control core. Open any product for specifications.

How the three work together
Security Command CenterLINX™ IQLINX™ 10 Enterprise
What it is Unified command and control platformOperator interface for mission controlIntrusion detection and access control platform
What it does Intrusion, access, video and cyber compliance in one viewShows the whole site in a 3D situational awareness planeVerifies operator commands cryptographically before they run
Where it runs Hardened workstations in the security operations centerOn the Security Command Center workstationIn the security operations center
Form Hardware: full size tower or compact miniSoftwareSoftware
Works with Includes LINX IQ, LINX 10 Enterprise, VICADS V100 and CSSLINX 10 Enterprise, with video from VICADS V100Universal Field Panels at the edge, and LINX IQ

Swipe horizontally to compare all three products

Where it sits

Unified Security Platforms span Purdue levels 0 to 3: from the IT and OT Operations layer, the security operations center where authenticated data arrives and operators act on it, down through Acquisition and Control to the devices at the OT Edge.

Explore the full architecture
  1. Enterprise Consumers Purdue 4 to 5
  2. IT and OT Operations Purdue 2 to 3
  3. Acquisition and Control Purdue 1
  4. OT EdgePSG embedded Purdue 0

How it works

Command and control on data you can trust

What unified means here

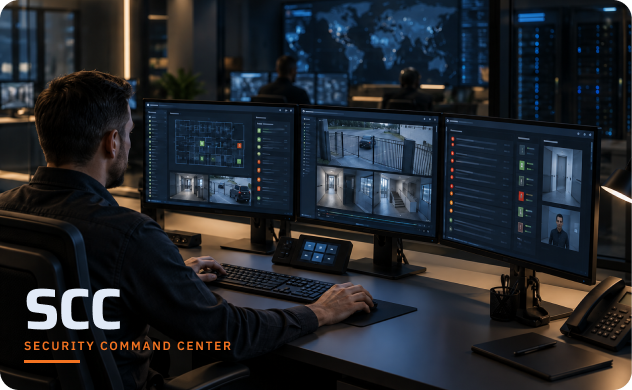
The Security Command Center is PSG's unified command and control platform. It includes LINX IQ, LINX 10 Enterprise, VICADS V100 and the CyberSecurity Solution, so intrusion detection, access control, verified video and cyber compliance run as one on hardened workstations. LINX IQ presents the site in three dimensions, so operators understand an event faster and respond without switching screens.

Why the platform trusts what it sees

PSG is the Embedded Zero Trust Architecture for Physical Security. Trust at the source is established below the platform: panels, controllers and Scene Authentication give each reader, sensor and camera a trusted device identity, and every event is authenticated before it moves up. Only verified data reaches the security operations center, so operators act on facts, not assumptions.

How operator commands stay verified

Verification runs in both directions. When an operator issues a command, such as unlocking a door, the chain of trust runs in reverse: the command and control platform must pass cryptographic tests before the command executes and changes anything in the field. Authenticated communications up and down the stack complete the chain of custody and protection.

How it fits with the systems you run

The same verified data that reaches the platform also feeds the SIEM and cloud systems above it, so enterprise analytics, digital twins and AI draw only on authenticated inputs. PSG's architecture is open, with standards-based protocols and a modern API. The devices beneath it upgrade input by input on existing wiring: modernization without rip-and-replace.

Utilities & Grid

Utilities & Grid

CIP-014 physical security for substations and generation.
Nuclear Power & DOE Sites

Nuclear Power & DOE Sites

Material protection, control and accounting.
Defense Installations

Defense Installations

PL1 through PL4, weapons storage and flight lines.

Specifying PSG?

Product pages carry the CSI section, data sheet and A&E resources for each product. Register for the A&E program for direct support from PSG systems engineers.

Register for the A&E program

One operator view, on verified data.

Tell us what you are protecting and what is installed. Visit with a PSG systems engineer about bringing intrusion, access and video into one view you can trust.